PHP Security Vulnerability: Updates for Entrust Card Printers
The recent PHP security vulnerability is a reminder that cybersecurity is not limited to servers and workstations. In fact, many connected devices, including card printers, use web interfaces and software components that must remain up to date. In October 2026, several critical vulnerabilities were discovered in the PHP scripting engine. Some of these vulnerabilities could allow an attacker to execute code on an affected device. Certain Entrust Datacard printers use a PHP-based web administration interface. Therefore, Entrust has identified corrective updates for the affected models. At Data Carte Concepts, we closely monitor security notices involving the products we distribute. As a result, we can proactively inform our customers and share solutions made available by the manufacturers.
Printers Affected by the Entrust Security Vulnerability
This issue is particularly relevant to the card printing industry. In fact, certain Entrust Datacard printers include a PHP-based web administration interface. According to technical information provided by Entrust, CVE-2026-109618 and CVE-2026-109619 could allow code to run on the printer. To exploit these vulnerabilities, an attacker would need access to the device’s web interface. Consequently, sensitive print job data could potentially be intercepted or manipulated. The affected printer families include: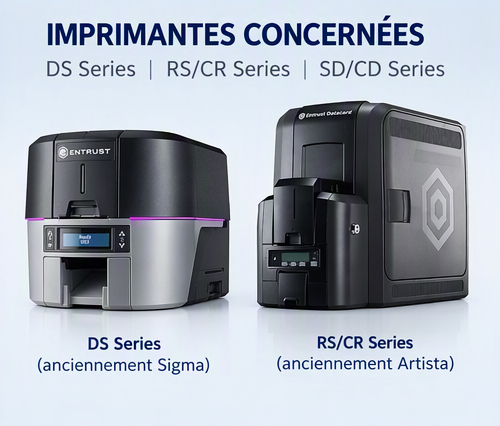
- Entrust Datacard DS Series, formerly Sigma, direct-to-card printers;
- Entrust Datacard RS/CR Series, formerly Artista, retransfer printers;
- Entrust Datacard SD/CD Series, legacy direct-to-card printers.
Network-connected printers are directly affected because of their web interfaces. USB-connected printers may also be affected, but only through local attacks or cross-site request forgery. However, CVE-2026-115560 does not affect these printers. Entrust states that the prerequisites for exploiting this vulnerability are not present.
Security Updates Provided by Entrust
To address the issue, Entrust identified specific corrective releases for each printer family:
- DS Series, formerly Sigma: D4.5.2-SP1
- RS/CR Series, formerly Artista: R4.14.1-SP1 or R4.54.1-SP1
- SD/CD Series: D3.20.2-SP1
According to the bulletin, Entrust expected the DS and RS/CR updates to be available by the end of October 28, 2026. The SD/CD update was expected by the end of November 4, 2026. Therefore, customers should confirm that the update for their printer model is available before proceeding. To download the latest firmware and drivers, follow the links below, then click the “View downloads” button:
- Support page for DS series printers
- Support page for RS/CR series printers
- Support page for SD/CD series printers
An Update Related to Digital Certificates
The update for DS Series printers also addresses a separate issue involving compromised private keys. Those keys belonged to certain intermediate certificate authorities operated by eMudhra. DS Series printers connect to Entrust to check for and download firmware updates. However, the impact of the compromised keys is limited because Entrust signs its firmware updates. Furthermore, the printers verify the signature before installing an update. Under certain circumstances, an attacker capable of intercepting the communication could interfere with the update verification process. For example, a printer could report that its firmware is current even when an update remains available. RS/CR and SD/CD Series printers are not affected by this specific certificate issue.
What If the Update Cannot Be Installed Immediately?
Entrust recommends applying the appropriate update as soon as possible. However, a temporary mitigation is available for organizations that cannot install it immediately. The mitigation consists of disabling the PHP-based web administration interface. As a result, exposure to the vulnerable interface is reduced. However, Entrust notes that re-enabling the interface may require assistance from technical support. Therefore, we recommend contacting our team before disabling this feature. We can help determine the appropriate approach for your printer model and environment.
Security Goes Beyond the Printer
This situation is a reminder that a network printer is also an IT device. Consequently, its security depends on several factors. A properly configured network remains important. However, organizations must also keep the printer’s firmware and embedded software components up to date. In addition, printers should operate on a trusted local network. Entrust identifies this type of environment as a mitigating factor. Nevertheless, network protection does not replace the recommended security updates. At the time of the bulletin, Entrust was not aware of any cases involving exploitation of these vulnerabilities among its customers. Even so, Entrust recommends applying the corrective updates as soon as possible.
Data Carte Concepts’ Commitment to Security
At Data Carte Concepts, our responsibility does not end when an identification solution is sold and installed. We place great importance on the digital security of the equipment our customers rely on. Therefore, when a manufacturer releases a security update for a product we distribute, we aim to share the relevant information promptly. In addition, we highlight the solutions made available by the manufacturers. This proactive approach is part of our commitment to supporting customers throughout the lifecycle of their equipment. Finally, whether the issue involves a security update, a new firmware release, or a technical problem, our team remains available. Our objective remains the same: to help customers maintain reliable, efficient, and secure identification solutions. Are you using an Entrust Datacard DS, RS/CR, or SD/CD printer? Contact our team to verify which updates apply to your equipment.